





Featured
Deep Dive Discovery & Posture
A Guide to Agent Control
Geordie’s Field Guide shows the control points Anthropic, OpenAI, AWS, and Microsoft have built in natively – and where each falls short.
Research, reference and long-form guides for the teams securing and running AI agents.
Featured
Geordie’s Field Guide shows the control points Anthropic, OpenAI, AWS, and Microsoft have built in natively – and where each falls short.
Plain answers to the questions teams ask about agents, MCP and skills.
By Topic
By Content Type
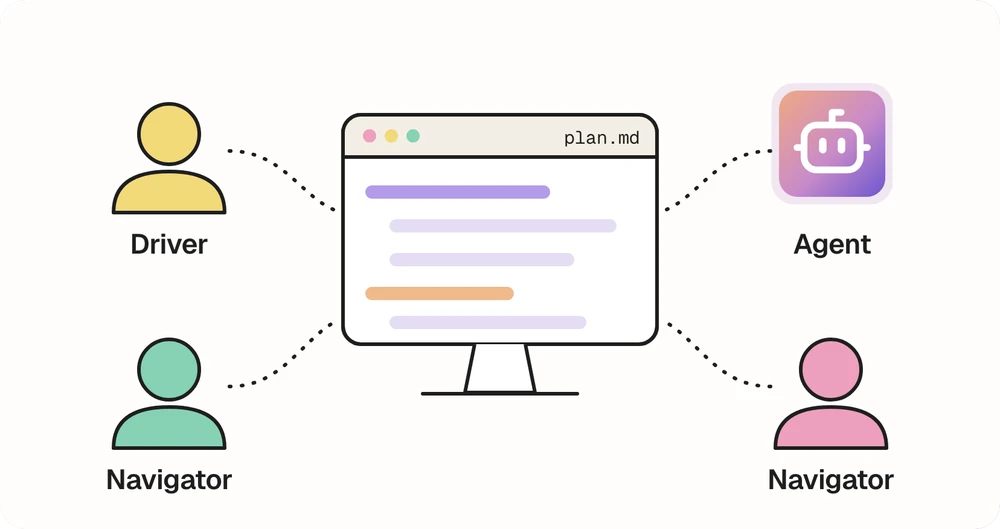
A few months of pairing and mobbing with agents later (mostly engineer with engineer, sometimes across disciplines), I think most of the core principles surrounding pairing matter even more.
Thirteen agent security & operations tasks, and who typically owns them.
Agents went from rogue pilots to essential workers in the space of two years, and several different ownership structures have emerged.
What do agents cost and deliver? Spend tied to the work agents perform, the value it returns and the risk security teams manage.
AI is becoming extraordinarily capable at tasks we associate with human intelligence.
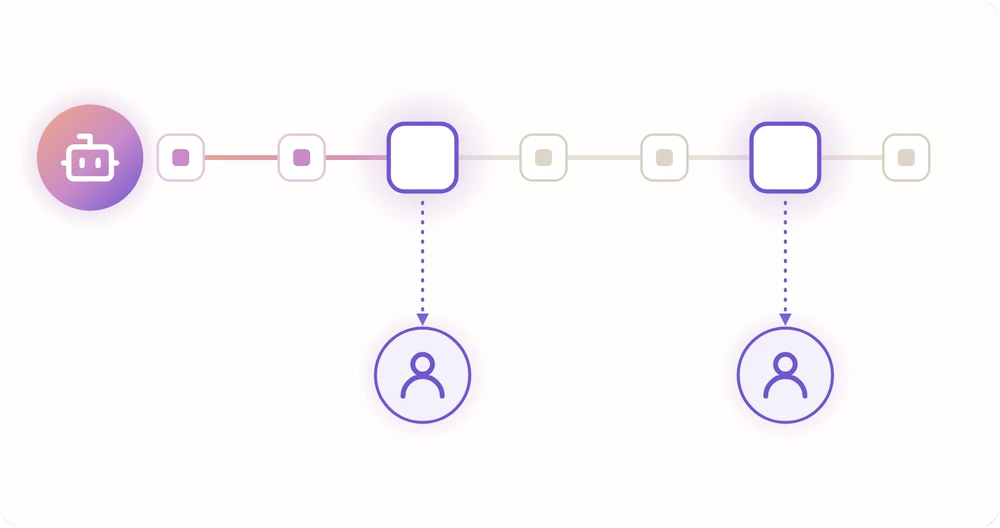
Human oversight is one of the most widely recommended safeguards for AI agents, yet putting a person in charge of approving an action says very little about whether they are equipped to exercise independent judgment.
The Claude Code extension for VS Code was trojanized at version 2.1.313 and distributed through the Cursor Extension Marketplace for about 11 hours, planting a persistent SSH backdoor.
How security leaders run an agent estate that is already doing the business's work, from the first inventory to a program that scales.
What did the agent actually do?
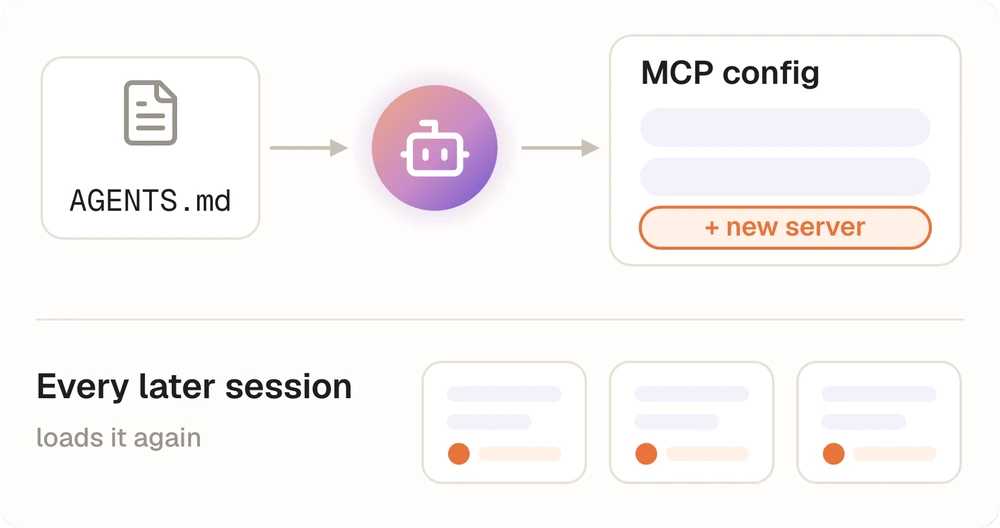
Security teams approve a coding agent by looking at how it is set up, which sandbox is on, which tools and MCP servers it can reach, and what it is allowed to run, and that approval rests on an assumption that the setup will still be the setup the next time anyone looks.
How do I reduce agent risk without stopping the work?
OWASP’s Q3 exploit roundup says prompt-level instructions alone do not establish a secure boundary.
Model capability is one input to what an agent does.
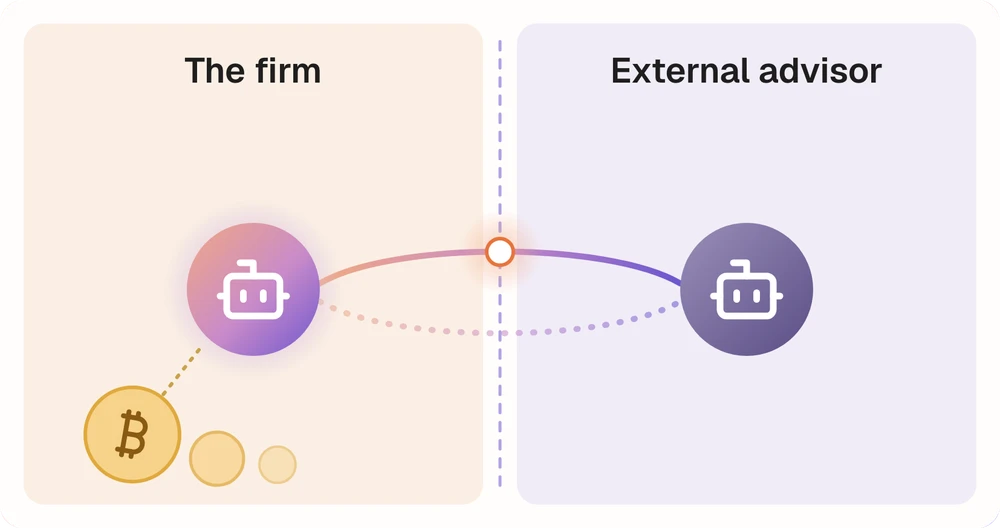
An AI agent was being used to mine Bitcoin.
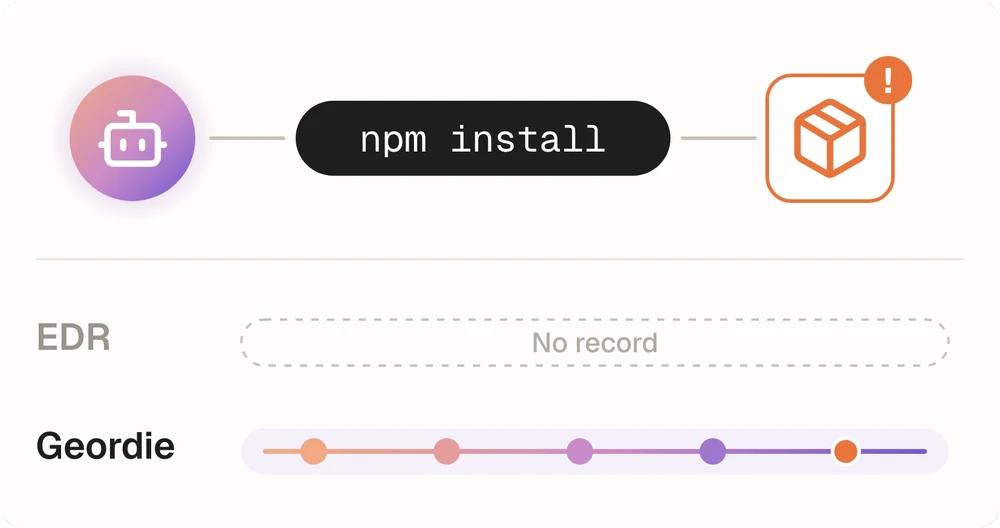
Their EDR had no record of the activity.
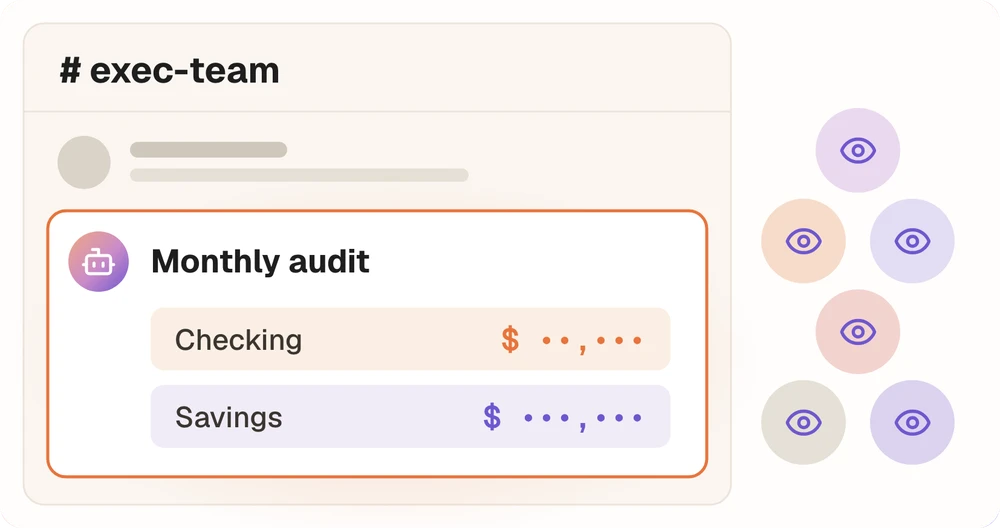
One personal agent posted a user's private financial audit into his company's exec Slack channel.
With agents our industry has a chain-of-custody problem.
Shane Mac’s account of an agent posting his bank balances into his company’s executive Slack channel is worth reading closely.
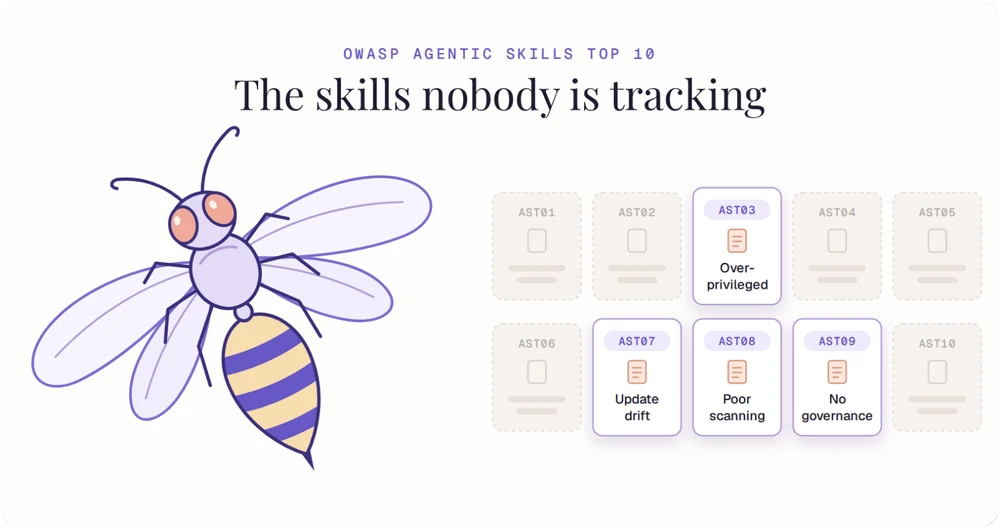
OWASP’s new Agentic Skills Top 10 gives security teams a shared vocabulary for agent skills.
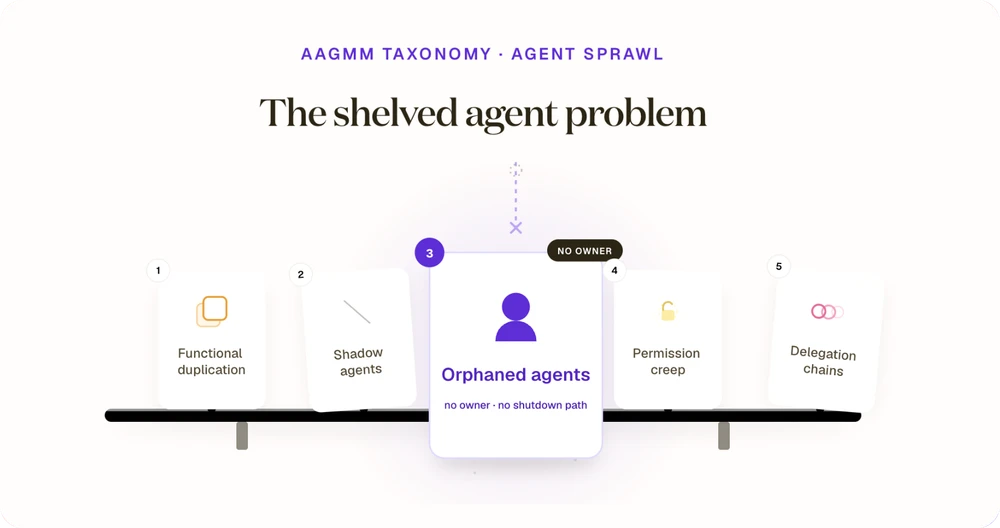
When enterprises iterate on their agent workflows, older agents rarely get decommissioned.
What 50+ organizations running agents in production told us about agent spend, who owns it, why the bill doesn't explain itself, and what to do instead of freezing.
Each agent security category extends the layer it was already built to watch.
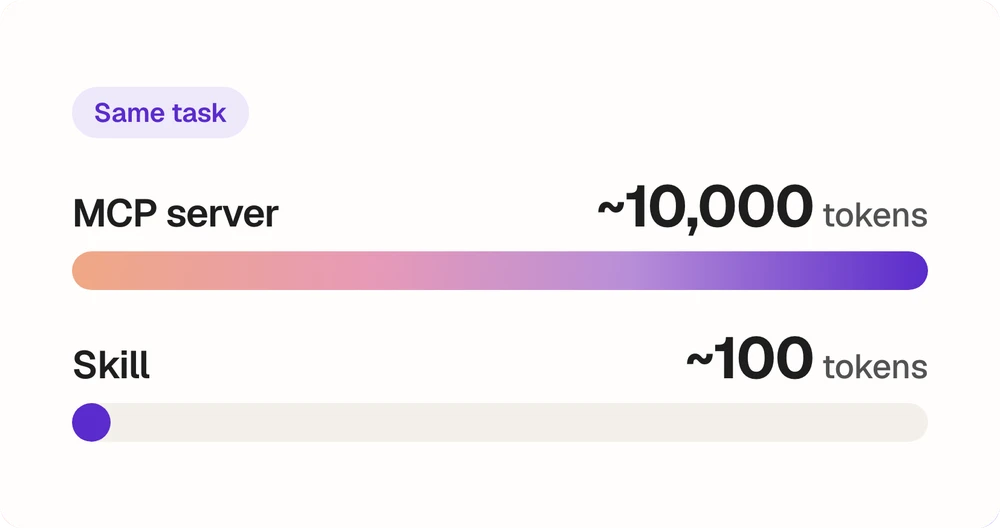
The same agent capability can cost ~10,000 tokens as an MCP server or ~100 as a skill.
Pre-approved agent template libraries optimize for control over a static asset, when the thing they're trying to control isn't static at all.
Move from uncertainty to informed confidence on both risk and spend, with cross-platform spend aggregation and token-efficiency mapping.
New capability gives AI Ops teams a clearer picture of the financial risk behind agent activity.
A malicious skill called Clawsights ran a shell command before Claude Code's model ever reasoned about it.
A working model for where agent skills actually create risk, and six practices for folding them into the governance you already run.
Geordie’s Field Guide shows the control points Anthropic, OpenAI, AWS, and Microsoft have built in natively – and where each falls short.
A new academic paper shows AI agents can be compromised without a single malicious instruction, just by corrupting what the agent trusts.
Four disclosures in three weeks, each one showing something new, all pointing to the same governance requirements.
What is new and what MCP 2.0 means for security teams
What this incident shows about governing AI agents
New collaboration gives GuidePoint customers access to purpose-built AI agent security and governance
Meet with the Geordie team at Black Hat USA 2026 in Las Vegas, August 1–6
The company’s unique approach to securing and governing AI agents drives 50× ARR growth in the first six months of 2026
How to adopt Cowork quicker using built-in configurations alongside contextual visibility and controls
Matching security and governance to teams moving fast on AI agent deployments.
Three foundational principles for governing the agentic toolset
A practical view of agent security from our work on OWASP's latest guidance.
Helping customers keep agent controls consistent as their infrastructure evolves.
AI agent security company sees 1300% ARR growth in the first five months of the year as global enterprises adopt at scale
Henry Comfort, CEO and co-founder of Geordie AI, on raising a $30M Series A and what it means for enterprises racing to govern autonomous AI agents.
Geordie is recognized for its achievements in Security and Governance for AI Agents
Geordie announces integration with Claude Compliance API to extend security and governance across the Claude Enterprise deployment surface
Go beyond identity to a broader maturity model of prompts, guardrails and behavior
Two Critical RCE flaws and five High-severity vulnerabilities in n8n, exploitable by any authenticated user.
Proactive security controls allow forward-looking teams to secure AI agents at scale
Prompt injection gets most of the attention in AI agent security.
A threat actor compromised the Trivy vulnerability scanner and used stolen CI/CD secrets to cascade into Checkmarx, LiteLLM, and 50+ npm packages.
Meet with the Geordie AI team at RSAC 2026 in San Francisco
Recognized for pioneering technology that enables enterprises to safely scale AI agents
Security researchers disclosed a tool chaining vulnerability in Claude Desktop Extensions rated CVSS 10/10, but this represents a known risk class in agentic AI systems – not a novel attack.
Authenticated attackers can escape n8n's Pyodide Python sandbox to execute arbitrary system commands with host privileges.
Critical unauthenticated remote code execution vulnerability in n8n workflow automation allows attackers to exploit content-type confusion in Form webhook file upload processing to read arbitrary files, steal credentials, and execute arbitrary code on the server.
Authenticated attackers can escape n8n's Pyodide Python sandbox to execute arbitrary system commands with host privileges.
Critical vulnerability in n8n workflow automation allows authenticated attackers to achieve remote code execution through Git node exploitation
Critical remote code execution vulnerability in n8n workflow automation platform allows authenticated users to execute arbitrary code on the server through specially crafted workflow expressions that escape the sandbox isolation.
A remote code execution vulnerability in Claude Desktop Extensions received a CVSS 10.0 score this week.
Guardrails are often treated as a universal safety layer for AI agents, but they're not.
Geordie AI selected for monitoring and governing AI agents in real time.
The autonomous nature of AI agents requires purpose-built agentic AI governance platforms.
AI Agents aren’t just software.
Building on research from Berkeley, this article outlines five barriers to enterprise AI adoption and the AI governance best practices to overcome them with visibility and accountability.
Building AI Agents promises speed and scale, but developers know the pitfalls.
Enterprises are experimenting with AI agents, but scaling safely requires enterprise AI governance.
APIs, MCPs, and A2A form the foundation of AI Agent systems, yet their roles are often fragmented.
Geordie won the Black Hat Europe 2025 Startup Spotlight.
A practical, deployment-level guide to patching recent mcp-server-git CVEs - explaining how uvx caching, pip installs, and outdated Docker images can leave systems vulnerable, and how to verify you’re actually fixed.
AI adoption is accelerating, but trust and accountability are essential.
What the next Model Context Protocol (MCP) release means for enterprise security and risk teams running AI agents in production.
ACE moves enterprise AI governance beyond static prompts to living playbooks.
Why OpenClaw matters less as a vulnerability story and more as a signal that personal autonomous agents have arrived.
Endpoint controls like EDR and XDR remain critical to enterprise defense, but they weren’t built for AI Agents.
AI adoption is accelerating, but not every investment is safe.
Eight high-to-critical n8n vulnerabilities disclosed in February 2026 invalidate earlier patching guidance.
As AI Agents evolve into autonomous actors, securing them requires techniques beyond identity and access controls.
A practical breakdown of recent n8n vulnerabilities, explaining exposure, risk, and how to choose the right remediation path.
AI Agents can’t be black boxes.
We started Geordie to build the governance layer for AI agents.
No resources match your filters.
We're exploring new ground... more coming very soon